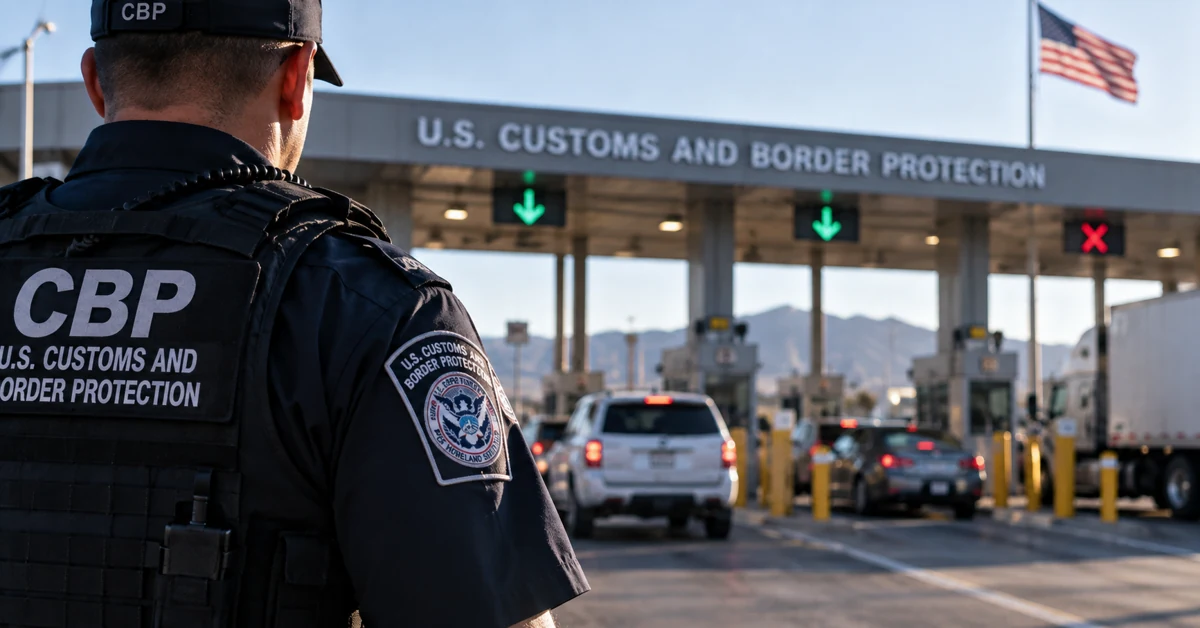
All 76,000 users on U.S. Customs and Border Protection’s network could access a single highly privileged service account capable of changing passwords, permissions and security settings, according to a Department of Homeland Security watchdog.
The vulnerability was introduced in 2019 and remained in place until the DHS Office of Inspector General uncovered it during its audit.
The account provided elevated access to systems operated by an agency responsible for approximately 100 major IT applications, including systems containing sensitive law-enforcement and biometric information.
The watchdog also found that all CBP network users had permissions that could enable privileged-account takeover.
The problems extended beyond the shared account.
Among accounts examined by the inspector general, 20% of sampled former employee accounts and 15% of identified contractor accounts were not disabled promptly after those individuals left.
Another 17% of identified employees who transferred elsewhere retained access they no longer required.
CBP accepted all 12 recommendations made by the watchdog.
Border control without access control
The finding is particularly striking because of what CBP does.
The agency operates at the centre of America’s border-security infrastructure and handles information that would be valuable to criminals, hostile states and other sophisticated attackers.
It has already experienced the consequences of being targeted.
Hackers stole CBP employee information in a June 2025 cyber incident.
Cybersecurity systems are supposed to operate on the principle of least privilege: users receive only the access necessary to perform their jobs.
CBP effectively achieved the opposite.
For around seven years, a workforce of 76,000 network users potentially had access to credentials powerful enough to alter some of the controls intended to protect the network itself.
An agency responsible for controlling who enters the United States failed one of cybersecurity’s most basic tests.
It failed to control who had privileged access inside its own systems.
Sources
Join the Dissenting Citizen Newsletter
Independent news and commentary delivered directly to your inbox.
Breaking stories, analysis and commentary throughout the day.
Follow @VoxDissent →